Building the Fintech Dream


The Latest Content
Do you actually know if your business is on the FIC's radar this year?
For a large number of gambling operators in South Africa, the honest answer is uncertain, and that uncertainty is the actual risk, not just an inconvenience. The FICA RCR deadline falling on 31 July isn't new territory for the Financial Intelligence Centre. The regulator ran this exact exercise before, under Directive 6, and institutions that ignored it or assumed it wasn't urgent ended up facing formal notices and sanctions once the FIC followed through.
That history matters because Directive 11 isn't asking for less this time. It's asking accountable institutions, gambling operators included, to prove they understand the money laundering and terrorist financing risk sitting inside their own business, not simply state that they do. If your business hasn't confirmed its FIC registration status, or isn't certain who internally is responsible for this submission, that gap needs closing well before the end of July, not during it.
FIC Directive 11 and the 2026 Risk and Compliance Return
FIC Directive 11 requires specified accountable institutions, gambling operators included, to submit a Risk and Compliance Return 2026 report to the Financial Intelligence Centre. This report asks businesses to self-assess two things: how well they understand their exposure to money laundering, terrorist financing, and proliferation financing, and how effective their actual controls are at managing that exposure.
A written policy sitting untouched in a compliance folder won't hold up here. The FIC isn't asking whether a programme exists on paper, it's asking whether the business can demonstrate that programme is actually working, and that gap between documented and demonstrated is exactly what the RCR is designed to expose.
Here's what the submission actually involves:
- To be submitted electronically through the FIC's goAML platform, not by email or hard copy
- To cover three years of activity, from 1 April 2023 to 31 March 2026, so historical data needs to be on hand, not just current records
- To be filed by 31 July 2026 for non-casino gambling institutions specifically
- Once filed, cannot be edited or withdrawn, which makes internal review before submission essential
Gambling Institutions FICA: Are You an Accountable Institution?
A lot of gambling businesses in South Africa don't realise they fall under FICA until a notice actually lands in their inbox, and by then the runway to prepare properly has already shortened considerably. Under Schedule 1 of the FIC Act, gambling institutions sit as Item 9, which places the entire sector under FICA obligations, covering all four legal forms of gambling recognised under the National Gambling Act, 2004. That means casinos, bingo, betting, and limited payout machines are all in scope, each one licensed by a Provincial Licensing Authority somewhere across South Africa's nine provinces.
The reasoning behind this classification comes down to how the industry actually operates. Cash moves quickly here, and stakes get placed and settled with very little friction between deposit and payout, which is precisely the kind of environment that makes gambling attractive for laundering illicit money. That's why the FIC applies the same level of seriousness to gambling operators as it does to legal practitioners and estate agents, rather than treating the sector as a lower priority.
Size doesn't change any of this either. A single-site bingo hall carries the same gambling institutions FICA status as a bookmaker with dozens of branches across the country. Whether the operation is small or large, the FICA compliance deadline South Africa businesses are racing against this July applies just the same.
Licensed and Compliant Are Not the Same Thing
Running a gambling operation in South Africa means satisfying two regulators with two entirely different mandates, and the complexity sits in managing both properly, not just knowing they exist.
The National Gambling Board handles licensing, through your Provincial Licensing Authority and its Verified Gambling Operators Web Portal. That confirms you're legally entitled to operate. It says nothing about money laundering risk.
The Financial Intelligence Centre asks a different question entirely. Not whether you're licensed, but whether you understand your money laundering, terrorist financing, and proliferation financing risk, and can prove your controls manage it, before the FICA RCR deadline arrives.
Both deserve equal attention. Your licence protects your right to operate, while your standing with the FIC protects you from sanction. That second obligation is exactly what the FICA compliance deadline South Africa has set for this July, and no approval from the NGB covers for it.
Preparing Your goAML RCR Submission
The FICA RCR deadline doesn't leave room for figuring things out as you go. A clean goAML RCR submission depends on groundwork most institutions underestimate until they're already behind on it.
Registration comes first, and it isn't optional:
- A valid FIC Org ID, issued through goAML, is required before the submission option is even available
- Outdated or incomplete registration needs correcting on its own timeline, well ahead of filing
Once registration is confirmed, preparation is what actually determines how smooth the submission goes:
- Review the FIC's sample questionnaire in advance, gambling institutions work from a sector-specific edition, not the generic composite version
- Pull together your Risk Management and Compliance Programme, customer due diligence records, and history of regulatory reports filed with the FIC
- Make sure this covers the full three year reporting period the RCR requires, not just the most recent year
A few rules govern the filing itself. Only a compliance officer, or someone with equivalent authority, can submit, third party providers are not permitted to file on an institution's behalf. And once submitted, the RCR is final, with no way to edit or withdraw it afterward.
What Missing the Deadline Actually Costs You?
Non-compliance under FICA carries formal, financial consequences, and gambling operators weighing whether this deadline is worth prioritising should know exactly what those consequences look like before deciding.
Section 45C of the FIC Act sets out what the FIC can actually do to a non-compliant institution:
- Financial penalties of up to R10 million for a natural person
- Financial penalties of up to R50 million for a legal entity
- Cautions and formal reprimands
- Remedial directives requiring specific corrective action
- Restrictions or suspension of business activities in serious cases
- Public disclosure of the sanction, unless compelling circumstances justify withholding it
Public disclosures are worth sitting with for a moment, because it changes what a sanction actually costs an operator. A financial penalty is a number that gets paid and eventually forgotten. A published sanction is different, it stays visible to banking partners, correspondent institutions, and other regulators long after the fine itself has been settled, and it shapes how those relationships treat the business going forward.
The numbers so far suggest a lot of institutions are still exposed to this risk.
Casinos, along with crypto platforms, trust companies, and credit providers, faced an earlier deadline of June 30th. But by mid-June 2026, the FIC reported a shockingly low compliance rate of just under 12%. As out of over 5,600 registered businesses across these sectors, a mere 655 had actually filed their returns.
Directive 6 already ran this exact process once. The FIC issued formal notices of intention to sanction against institutions that failed to submit, and that enforcement record is the clearest signal available for how seriously the current Directive 11 gambling deadline will be treated. Nothing here is speculative. It's a repeat of a process the regulator has already carried out, with documented consequences for the institutions that didn't take it seriously the first time.
Gambling operators carry a particular exposure here that other sectors don't share as sharply, since the industry already moves large volumes of cash through rapid transactions, exactly the profile the FIC treats as elevated risk. An operator that files late, or not at all, doesn't just sit outside the rules on paper. It gets flagged into precisely the risk category this entire system was designed to identify.
Meeting the FICA Compliance Deadline South Africa
The FICA compliance deadline South Africa has set for gambling operators this year rewards preparation. It penalises delay just as clearly. There's very little middle ground between the two.
Registration needs to be sorted well before July. Sector-specific documentation needs to be gathered. Risk Management and Compliance Programme records need to be in order, not assembled under pressure once the submission window is closing.
FlexM has spent over a decade building compliance infrastructure for regulated and non-regulated entities across the globe, including South Africa, which is what makes FlexComply relevant here. The platform brings risk assessment, transaction monitoring, and regulatory reporting into one system, so operators aren't piecing together evidence from scattered records when a deadline like this one arrives.
Meeting this deadline isn't just about avoiding a sanction. It's what keeps a gambling business operating with the full confidence of its regulator, its banking partners, and the market it serves.
What if your fraud prevention controls are working exactly as designed, and that is precisely the problem?
Across the United States, risk and compliance teams are closing cases, clearing alerts, and reporting fraud losses within acceptable thresholds, while a completely different category of financial crime is scaling invisibly underneath those metrics.
Most AI fraud prevention strategies in use today were built around human fraudsters making human mistakes and leaving human traces. But the dominant fraud threat of 2026 is not human. It is algorithmically generated, behaviorally convincing, and specifically engineered to look clean inside the very systems designed to catch it. Synthetic identity fraud alone is projected to cost US businesses between $30 and $35 billion annually, and it now accounts for up to 80% of all new account fraud, yet represents only 4% of fraud cases by frequency. That gap between frequency and financial impact is exactly what makes it so dangerous and so difficult to act on.
The uncomfortable reality is that AI has not just changed how fraud is committed. It has fundamentally changed what fraud looks like.
AI-Driven Fraud Is Rewriting Financial Crime in the US
For most of the past decade, fraud in the United States followed a recognisable pattern. A stolen credential, a compromised account, a suspicious transaction that triggered an alert. The tools built to catch it were designed around that pattern, and for a long time they worked reasonably well. That era is over.
Fraudsters in 2026 are operating AI systems that run continuously, adapt in real time, and are specifically engineered to exploit the gaps in conventional fraud detection and prevention infrastructure. These are not isolated criminal actors making opportunistic moves. They are organised networks deploying machine learning to manufacture false identities, generate convincing synthetic documents, and automate attacks at a scale that human review cycles simply cannot match.
What this shift looks like in numbers:
- US businesses reported losing 9.8% of annual revenue to fraud in 2025
- AI-enabled fraud losses are projected to reach US$40 billion in US by 2027
These are not numbers that reflect a problem under control. They reflect a problem that has been consistently underestimated because the most damaging fraud category barely registers in case frequency data while quietly driving an outsized share of total financial losses.
Synthetic Identity and Deepfakes: One Industrialised Threat
Generative AI has given fraudsters something they never previously had, which is the ability to manufacture a believable human identity at scale and use it to systematically extract money from financial systems over an extended period of time.
A synthetic identity fraud profile combines real data fragments, typically a legitimate Social Security number paired with a fabricated name, address and contact details, to create a person who does not exist but passes every standard verification check. This identity is then used to open financial accounts, build a credit history through months of normal-looking activity, and steadily increase available credit limits until the fraudster decides the ceiling is high enough. At that point every credit line is maxed simultaneously, the funds are moved and the identity is discarded, leaving no real victim to file a report and no trail meaningful enough to follow.
The one control that historically stood between a synthetic identity and a fully operational account was biometric verification. Deepfake technology has made that control increasingly unreliable:
- Fraud attempts leveraging deepfake content have climbed more than 2,137% over the last three years
- Around 1 in every 5 biometric fraud attempts now involves face swaps or animated selfie manipulation engineered specifically to defeat liveness detection
- Only 13% of companies currently run any anti-deepfake protocols, meaning the vast majority of US businesses are encountering this threat without a specific defense against it
These are not two separate problems requiring two separate responses. They are sequential steps in the same industrialised pipeline, and together they have made AI-driven fraud detection one of the most urgent and least solved challenges in US financial services today.
Detect deepfakes. Block synthetic identities.
Synthetic identities are not just used to access credit. They are used to build the infrastructure through which fraudulent funds move internationally:
- Money mule networks exploit remittance corridors specifically because monitoring across jurisdictions is fragmented
- Each leg of a cross-border transaction obscures the origin of funds further, making the trail progressively harder to follow
- By the time a suspicious pattern surfaces, the money has typically already cleared several intermediary accounts across multiple geographies
The regulatory environment adds further pressure on US businesses managing cross-border flows:
- FinCEN requirements, OFAC sanctions obligations and state-level MSB regulations each carry distinct monitoring and reporting demands
- Businesses handling high transaction volumes across multiple corridors carry significant exposure when these are treated as separate obligations rather than a connected compliance framework
- Fraud monitoring and regulatory compliance handled in silos means organised fraud networks find the gaps before you do
Effective cross-border remittance fraud prevention was never about more tools. It was always about a single connected view.
Why Traditional Fraud Prevention Software Is Failing
The fundamental problem with most fraud prevention software currently in use across the US is not that it is poorly built. It is that it was built for a different threat environment entirely.
The Fraud Detection Gap:
When fraud is specifically designed to look normal, a system built to detect abnormality will consistently miss it. Rule-based transaction monitoring flags anomalies based on predefined patterns. Synthetic identities do not produce anomalies. They produce clean transaction histories, healthy credit scores and behaviours that look entirely legitimate until the moment they do not.
Traditional adverse media screening faces the same structural problem. Keyword-based systems flag anyone mentioned near a negative term regardless of their actual role in the story. A judge presiding over a fraud trial triggers the same alert as the defendant. Hundred articles covering the same incident generate hundred separate alerts. The result is alert fatigue that is not just an operational inconvenience but a genuine compliance risk, because when analysts are buried in noise, the signals that actually matter get missed. AI-driven fraud detection systems have demonstrated the ability to reduce false positives by 65 to 90%, which gives a reasonable indication of how much noise currently exists inside conventional systems.
What Effective AI Fraud Prevention Looks Like in Practice?
Genuine AI fraud prevention in 2026 is not about replacing one set of rules with a smarter set of rules. It is about understanding context, behaviour and risk continuously, across the entire customer lifecycle.
Behavioral intelligence over transaction rules
- Builds a continuous model of how each customer normally operates
- Detects deviations from individual behavioral baselines, not just known fraud patterns
- Catches synthetic identity bust-outs before execution because the behavioral shift preceding them is visible even when the transaction looks routine
Context-aware AI adverse media screening
- Distinguishes between a perpetrator, witness, judicial authority and victim mentioned in the same article
- Clusters related coverage of the same event into a single alert rather than one notification per publication
- Tracks event progression from investigation through to conviction, updating risk profiles dynamically
Perpetual KYC
- Replaces point-in-time onboarding snapshots with continuously updated customer risk profiles
- Triggers reviews when risk signals change rather than waiting for scheduled periodic reviews months away
Real-time fraud monitoring
- Real-time systems prevent substantially higher fraudulent transactions than batch-based processing
- When synthetic identities execute bust-outs across hundreds of accounts simultaneously, the difference between real-time and near-real-time detection is measured in millions of dollars
The businesses best positioned to handle AI-driven fraud are not those with the most tools. They are those with the most integrated tools, where identity verification, screening, behavioral analytics, transaction monitoring, threshold monitoring and regulatory reporting function as a single connected system rather than separate functions with blind spots between them.
Your 2026 Fraud Prevention Checklist
Before your next compliance or risk review, work through these:
- Are your fraud controls built around behavioral signals or purely transaction rules?
- Can your adverse media screening distinguish between a perpetrator and a witness in the same news article?
- Does your cross-border payment monitoring operate as a unified layer or as separate domestic and international functions?
- Are your customer risk profiles updated continuously or only at scheduled review intervals?
- Have you assessed your exposure to deepfake-enabled verification bypass attempts?
- Does your fraud monitoring cover behavioral and device intelligence beyond transaction data alone?
- Can your system detect synthetic identity patterns before a bust-out rather than after?
The Cost of Standing Still Is No Longer Acceptable
The fraud environment facing US businesses in 2026 demands a response that matches the sophistication of the threat. The businesses that navigate this successfully will be those that treat fraud detection and prevention as a unified, AI-powered function rather than a collection of point solutions that communicate only when something has already gone wrong.
FlexM, a leading global fintech conglomerate trusted by over 400+ businesses across the world, has spent over a decade building exactly this kind of integrated infrastructure, purpose-built for the complexity that modern financial crime demands.
The conversations happening this week at New York Fintech Week 2026 in Manhattan, among founders, risk leaders and compliance heads, reflect precisely the urgency that businesses across the US are waking up to. Fraud prevention in an AI-driven world is no longer a back-office compliance exercise. It is a strategic business priority, and the question every US business needs to answer is whether their defenses were built for the version of fraud that already exists today.
Identify gaps across behavior, identity, and real-time risk detection

When Nigeria exited the FATF grey list in October 2025, it was a defining moment for the country's financial system. Years of regulatory reform, institutional coordination and political will had finally paid off. But that exit was never meant to be a finish line. It was a starting point.
The CBN's March 2026 circular has made that unmistakably clear. Every regulated financial institution in Nigeria, from deposit money banks to mobile money operators to payment service providers, must now deploy automated AML solutions that meet new CBN AML requirements 2026. And the first critical deadline is already around the corner: implementation roadmaps must be submitted to the CBN's Compliance Department by June 10, 2026.
For compliance leaders who have spent years navigating manual processes, fragmented systems and growing regulatory expectations, this circular changes the game. It is the most consequential financial crime compliance directive Nigeria has seen in years, and it demands a level of technological readiness that most institutions have not yet achieved.
What Has the CBN Mandated and Who Does It Apply To?
The CBN's March 2026 circular (referenced as BSD/DIR/PUB/LAB/019/002), establishes mandatory CBN baseline standards for AML across the entire regulated financial sector. These standards apply to all financial institutions currently operating under CBN regulation; furthermore, applicants for new licenses must also demonstrate compliance or present a credible implementation plan as part of the authorization process.
The circular introduces three compliance milestones that every institution needs to plan around:
The implementation roadmap is more than a plan; it is a formal regulatory submission that demands absolute precision. To satisfy this requirement, the document must include:
- A current-state assessment and gap analysis to pinpoint specific vulnerabilities.
- The proposed AML solution architecture.
- A phased timeline featuring named milestones and clear owners for every workstream.
- A robust governance and oversight framework.
- A committed resource and budget plan.
This submission requires the highest level of internal accountability, finalized with the signatures of both the CEO and the Chief Compliance Officer.
The CBN is clear that compliance is not a checkbox exercise. The regulator will evaluate demonstrable effectiveness rather than vendor-driven implementation. In practice, simply having a system in place is no longer the benchmark. The regulator now requires proof that the solution delivers measurable results in:
- Detecting complex financial crime patterns.
- Facilitating thorough investigations.
- Maintaining precise, timely reporting.
The 12 Baseline Capabilities That Will Define CBN Compliance 2026
The circular sets out 12 capability areas that every automated AML solution must support. For institutions still relying on manual processes or disconnected point solutions, this list serves as the definitive benchmark against which the CBN will measure readiness.
One requirement in the circular is worth highlighting separately. The CBN has explicitly stated that AML solutions operating solely on transaction data, without effective linkage to customer identity, risk profiles and case histories, will not be considered compliant. Institutions rated High or Above Average risk within their subsector are specifically required to ensure full integration between their AML systems and their KYC/KYB repositories. This effectively ends the era of siloed compliance architecture in Nigeria's financial sector.
Get Your Free Guide
A complete, easy-to-use guide for your gap analysis
Why Is This Circular Different from Previous Nigeria AML Regulations?
Nigerian financial institutions have seen plenty of regulatory updates over the years. So what makes this one stand out?
- Accountability now sits at the top
Compliance is no longer just an institutional responsibility. The circular makes it clear that board members, CEOs, and Chief Compliance Officers can be held personally accountable. A compliance failure is now a direct leadership risk.
- Explainable AI is a regulatory requirement
The CBN has formally introduced AI and machine learning governance into its AML framework. Institutions must deploy automated AML systems, with expectations scaled to their size and risk profile.- Larger institutions are expected to use advanced AI-driven systems
- Smaller institutions can adopt proportionate solutions, but must still meet baseline requirements
- Strict AI governance expectations apply
Any use of AI or ML must include:- Human oversight
- Algorithm transparency and explainability
- Clear reasoning behind every alert generated
- Independent validation at least annually, covering accuracy, drift, fairness, and bias
- FATF Compliance depends on execution
Nigeria’s exit from the FATF grey list was a major milestone. This circular is about sustaining that progress. The CBN is signalling that compliance must be continuous, measurable, and evolving to maintain global credibility.
What Is Actually Holding Institutions Back?
The directive is clear and well-structured. But across the sector, readiness remains a significant concern. What are compliance teams actually up against?
The fraud numbers reinforce the urgency. Nigerian banks lost ₦3.3 billion to fraud in the first quarter of 2025 alone, a 137% increase from ₦1.39 billion in the previous quarter. For institutions still managing financial crime compliance Nigeria requirements through manual and fragmented setups, the risk of falling behind is not theoretical.
Disconnected systems are still common. Identity verification and AML processes often run on separate platforms with limited data sharing. The CBN requires integration across AML systems, core banking, and KYC or KYB data to enable a unified customer view.
The CBN also encourages a unified financial crime setup where AML and fraud systems share risk signals. This means many institutions must rethink how their systems connect and operate.
Too many tools, not enough integration. Nigeria’s RegTech market has expanded, but many solutions are single-purpose. Institutions need to assess vendors based on API capabilities, integration depth, and their ability to support end-to-end compliance needs.
A Step-by-Step CBN Compliance Roadmap to Get Ready Before June 2026
With the June 10 deadline approaching, institutions need a structured approach that meets CBN expectations and supports long-term compliance.
Start with a clear gap analysis. Map your current capabilities against the 12 baseline areas in the circular. Identify what is compliant, where gaps exist, and where systems are misaligned. This forms the foundation for all next steps.
Evaluate system integration. Does your AML case management system connect to your KYC records and customer risk profiles? Does your transaction monitoring engine assess activity within the context of the full customer profile, or does it operate on raw transaction data alone? The CBN has stated clearly that the latter approach is not acceptable.
Prioritise near real-time screening and monitoring. This includes sanctions screening, PEP checks with fuzzy matching, suspicious activity detection across channels, and the ability to block onboarding or transactions instantly when needed. Batch processing is no longer sufficient.
Prepare a Board-authorised implementation roadmap. This must be submitted to the CBN Compliance Department by June 10. Include your gap analysis, solution architecture, phased timeline, governance framework, and sign-off from the CEO and Chief Compliance Officer.
Embed AI governance early. If using AI or ML for risk scoring or detection, document validation processes, explainability standards, and bias testing. The CBN expects outputs that investigators can clearly interpret.
Focus on continuous compliance. The CBN will monitor through ongoing reviews and examinations. Institutions that build for transparency, governance, and continuous improvement will be better positioned than those treating this as a one-time task.
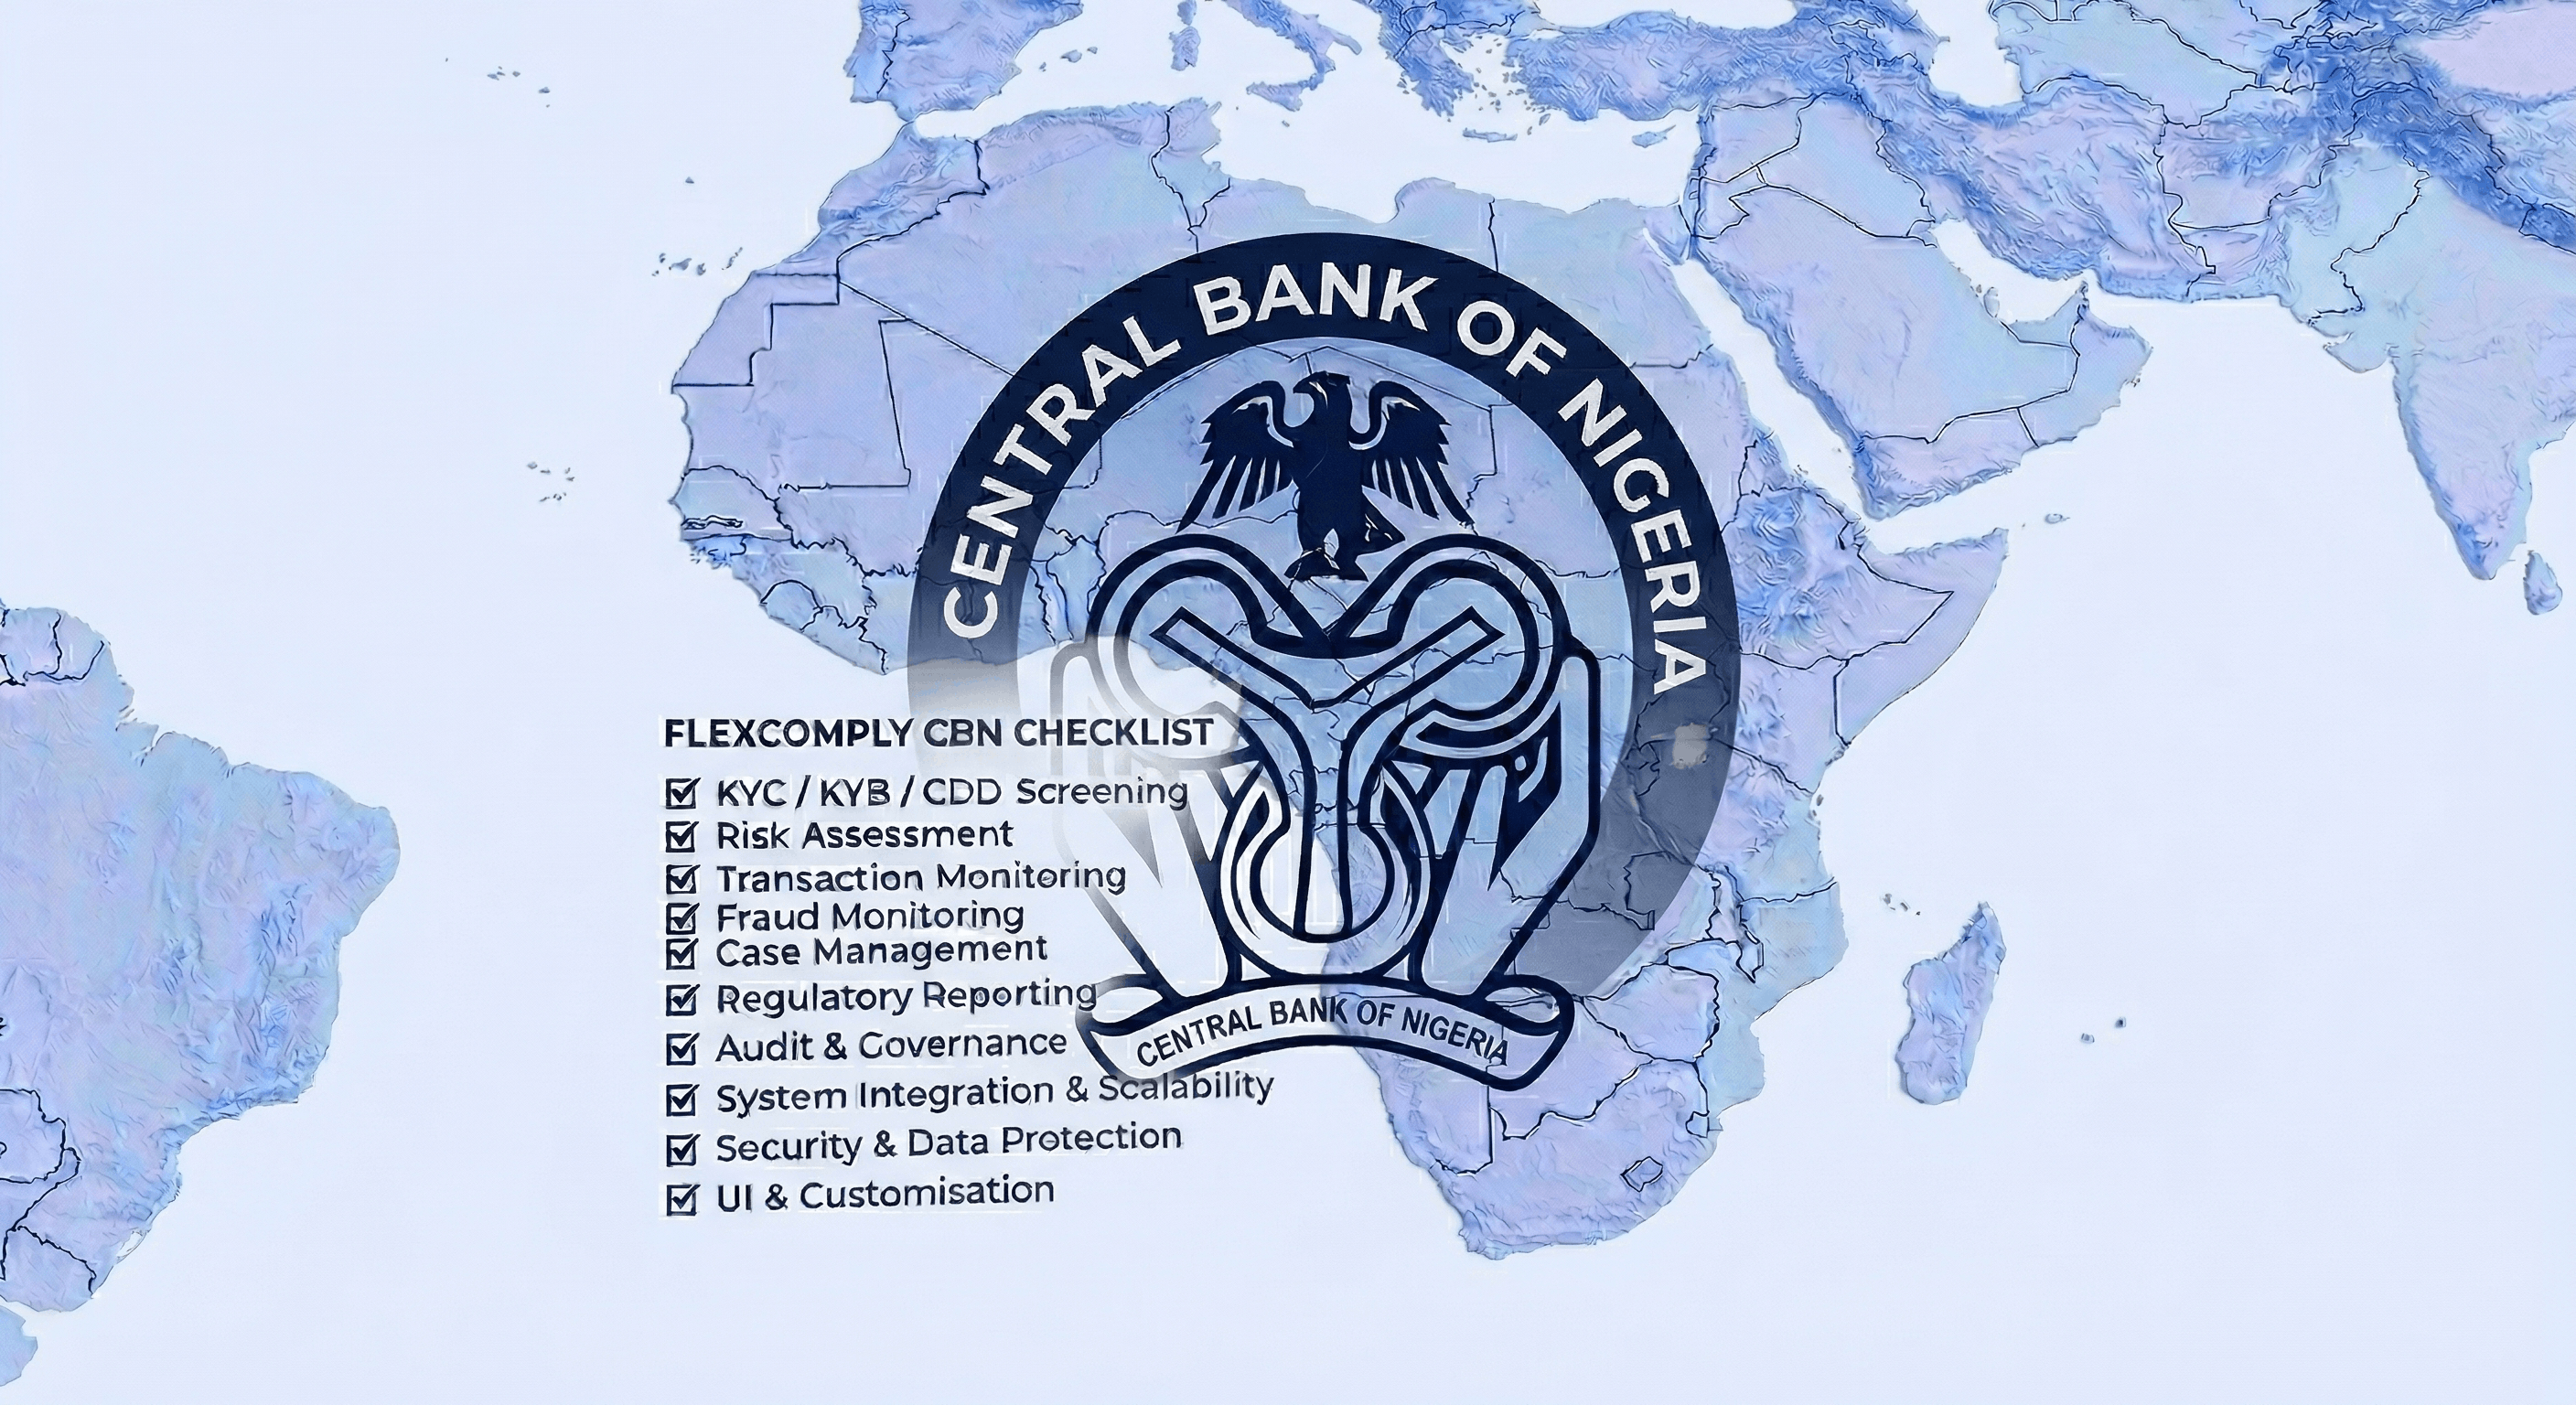
Building Compliance Infrastructure That Outlasts the Deadline
The institutions that will emerge strongest from this transition are those that see the CBN's March 2026 circular not as a regulatory burden but as a catalyst to build compliance infrastructure that delivers lasting value.
FlexM, the leading global fintech conglomerate, offers FlexComply, a 360-degree compliance technology platform designed for exactly this and beyond. As a unified FRAML platform, FlexComply addresses all 12 CBN AML requirements 2026 within a single integrated infrastructure.
Furthermore, FlexComply's AI-powered adverse media screening goes beyond keyword-based matching, using context-aware entity recognition and role-based adversity logic to deliver high-precision alerts with significantly fewer false positives. In a regulatory environment where the CBN now expects explainable AI outputs and continuous monitoring as part of its baseline standards, this capability is no longer optional.
CBN compliance 2026 is not about meeting a single deadline. It is about building the kind of financial crime compliance architecture that earns confidence from regulators, international partners and customers for years to come.
Ready to see where your institution stands against the CBN's 12 baseline requirements?
Get a tailored compliance gap analysis. No sales pitch, just expertise
Money Service Businesses sit at the center of an increasingly complex financial ecosystem. They move value across borders, connect legacy finance with emerging fintech models, and serve millions of customers who rely on fast, compliant and reliable services. But as the sector expands, so do its operational and regulatory vulnerabilities. Even well-established MSBs are finding that growth exposes gaps their legacy systems cannot absorb — a pattern consistently highlighted by leading global fintech conglomerates like FlexM, whose modular platform architecture is built specifically for MSB scalability. In this environment, choosing a scalable Money Service Business platform has become a structural, not optional, decision.
The Industry Has Outgrown Its Traditional Infrastructure
Money Service Businesses now operate within one of the fastest-expanding and most complex financial environments in the world. The scale of value moving across borders has fundamentally shifted. The global cross-border payments landscape is projected to reach US $290 trillion by 2030, signalling not only rapid expansion but also an urgent need for more resilient, intelligent infrastructures capable of supporting such unprecedented flows.
At the same time, the global remittance market — a core operational channel for MSBs — is expected to reach US $744.8 billion in 2025. This surge highlights just how central MSBs have become to cross-border value movement, financial inclusion, and alternative financial rails.
Yet despite this scale, MSBs often operate on outdated, fragmented systems built for a different era. Manual onboarding, spreadsheet-driven reconciliations, disconnected AML tools, and channel-specific workflows all create bottlenecks that compound as the business grows. A modern money service business software resolves these limitations by creating a unified ecosystem where customer onboarding, risk scoring, monitoring, and reporting operate cohesively rather than in silos.
Regulation Has Entered a New Phase — and Money Service Business Platform Are on the Front Line
Compliance is no longer episodic; it is continuous.
The most significant example of this shift came in October 2025, when Canada introduced sweeping AML reforms that tighten MSB registration, strengthen sanctions-reporting requirements, and elevate expectations for transaction traceability and governance oversight. These changes signal an international trend: regulators expect MSBs to demonstrate control, transparency, and auditability at the same level as major financial institutions.
This rise in scrutiny makes a scalable MSB compliance platform indispensable. Instead of retrofitting new rules into legacy processes, MSBs require systems that adapt in real time — recalibrating workflows, updating risk logic, recording audit trails, and supporting ongoing monitoring automatically. FlexM’s modular compliance stack, for example, enables MSBs to adjust rapidly to regulatory shifts without operational disruption.
How a Unified MSB management system Reduces Operational Risk
While regulatory pressure is highly visible, operational strain often becomes the hidden obstacle that prevents MSBs from scaling. As MSBs add new corridors, payout partners, digital channels, agent networks, and customer types, their internal complexity grows exponentially.
This increased complexity typically manifests as:
- inconsistent onboarding decisions
- duplicated customer records across systems
- slow case resolution due to manual reviews
- siloed data resulting in incomplete risk views
- rising operational cost as teams expand linearly with volume
A scalable MSB management system alleviates these issues by consolidating data, automating repetitive workflows, standardizing decision logic, and giving compliance and operations teams a unified real-time view of customer and transaction activity. This reduces cost-to-serve, lowers error rates, and allows MSBs to expand sustainably.
Customer Experience Has Become the Real Test of Modern money service business software
Modern MSB customers expect:
- fast, seamless onboarding
- real-time transaction visibility
- consistent decisioning
- predictable turnaround times
- omnichannel continuity
Whether these customers are individuals, SMEs, marketplaces, or digital platforms, they expect immediacy and clarity — expectations that strain fragmented systems.
A unified money service business software ensures that customer journeys remain consistent even under heavy transaction loads. FlexM’s customer-centric architecture demonstrates how MSBs can maintain service standards while supporting complex multi-corridor, multi-partner environments.
Why Scalability Defines the Next Generation of MSB Leaders
For MSBs, scalability means far more than handling additional volume. It means:
- Regulatory scalability: adapts to new rules, jurisdictions, and reporting structures without painful system rebuilds.
- Operational scalability: workflows remain stable and efficient as activity multiplies.
- Risk scalability: monitoring improves with scale, rather than degrading under pressure.
- Customer scalability: experience quality remains consistent across channels and growth cycles.
- Technology scalability: infrastructure remains reliable during peak loads and expansion phases.
This is the type of scalability required to survive the next decade of regulatory and competitive transformation.
Scalable Money Service Business Platform: The New Competitive Edge
The MSB industry is entering its defining period. Transaction volumes are rising, compliance expectations are intensifying, and customer journeys are becoming more digital and demanding. A scalable Money Service Business platform is no longer an optional upgrade. It is the backbone of MSBs that intend not only to grow, but to lead in a sector where resilience, adaptability, and compliance readiness define long-term success.
FlexM’s modular ecosystem — both compliance, and remittance — gives MSBs a single, integrated foundation built for real-world scale. Discover how your MSB can modernize with confidence: visit flexm.com to learn more.
In today’s hyper-regulated financial landscape, compliance is not just a checkbox—it’s the backbone of operational trust and long-term scalability. For fintechs, money service businesses (MSBs), and emerging digital banks, the ability to manage compliance seamlessly is critical to sustainable growth.
Financial institutions spend billions annually on compliance. The overall market for financial crime compliance is projected to reach over $55.47 billion by 2032, indicating a massive increase in spending and a growing reliance on technology to manage these costs. This makes selecting the best compliance management software for fintech not only a strategic choice but also a competitive differentiator. FlexM, a leading global fintech conglomerate, with its award-winning compliance platform, FlexComply, has been at the forefront of empowering regulated entities to simplify compliance while scaling with confidence.

The Rising Importance of Compliance in Fintech
Early enforcement actions in 2025 show regulators intensifying their focus on fintechs, neobanks, and digital financial platforms. In the U.S., LPL Financial received a $3 million FINRA penalty for AML failures tied to penny stock surveillance, while Block Inc. (Cash App) faced a coordinated $80 million multi-state enforcement action for BSA/AML program deficiencies. These early cases signal a proactive regulatory stance toward emerging financial platforms and newer risk vectors across the digital finance ecosystem.
As fintechs expand across borders, compliance demands become more complex—spanning AML/CFT obligations, data protection laws, and dynamic KYC/KYB requirements. The challenge is no longer just about adhering to regulations; it’s about doing so efficiently, without stifling innovation. That’s where compliance management solutions steps in—integrating automation, AI, and analytics to transform risk oversight into a proactive advantage.
Fintech startup platforms Singapore and across Asia, for instance, face some of the world’s most rigorous compliance standards under the Monetary Authority of Singapore (MAS). For such players, adopting a scalable fintech platform for MSBs ensures alignment with multiple jurisdictions while minimizing manual oversight. The goal is to stay audit-ready, reduce false positives, and improve decision-making—all through a unified compliance lens.
Key Features to Look For
- Comprehensive Identity Verification
A good compliance solution must support real-time KYC/KYB verification, This not only enhances user trust but accelerates onboarding without compromising regulatory requirements.
- Automated Screening & Monitoring
Continuous screening against global sanctions, PEPs, and adverse media lists is vital. The best compliance management software for fintech automates these checks, offering ongoing monitoring that updates dynamically as new data emerges.
- Risk-Based Assessment Frameworks
Fintechs need adaptive risk scoring—factoring customer behavior, geography, and transaction velocity. Scalable platforms can customize these rules to fit business models while staying regulatorily compliant.
- Transaction and Threshold Monitoring
Smart monitoring tools detect unusual activities in real time, flagging suspicious transactions before they escalate. Automation helps teams prioritize alerts based on severity rather than volume.
- Regulatory Reporting & Case Management
Automated STR/SAR generation, complete audit trails, and unified case management dashboards make investigations faster and more transparent—
- Automation-Driven Analytics
Machine learning can predict emerging compliance risks by analyzing patterns across customer segments and jurisdictions.
How Scalability Shapes Compliance Success
Startups often choose tools that solve immediate problems, but as they expand, they realize the need for scalable, modular solutions. A modular banking infrastructure fintech approach enables seamless integration of new regulatory features, APIs, and data models without overhauling existing systems. This agility ensures fintechs can stay compliant as they grow—launching new products, entering new markets, or integrating with new payment networks.
FlexComply, for example, has built its compliance framework to scale effortlessly with clients’ business growth. Its modular architecture lets financial institutions integrate compliance modules—such as AML, transaction monitoring, or UBO discovery—individually or as a full suite. This flexibility allows MSBs and digital banks to tailor solutions to their specific operational needs.
The Future of Compliance Solutions in Fintech
The next generation of compliance management will focus on predictive intelligence—systems that flag potential breaches before they happen. Cloud-native solutions, AI dashboards, and perpetual KYC frameworks will redefine compliance from reactive to anticipatory. Moreover, as digital identity standards evolve globally, interoperability between fintech ecosystems will become a compliance mandate in itself.
FlexComply continues to embody this vision—merging compliance, scalability, and innovation into a single, unified ecosystem. For fintech startup platforms Singapore and beyond, this marks the evolution from manual monitoring to intelligent, data-driven governance.
Final Thoughts
As fintechs expand across borders and digital financial ecosystems grow more complex, compliance can no longer function as a reactive function—it must operate as a strategic engine for trust, growth, and operational resilience. Choosing the best compliance management software for fintech is ultimately about enabling scale without sacrificing regulatory integrity. For MSBs navigating high-volume, multi-corridor environments, only a scalable fintech platform for MSBs can support the pace, risk, and oversight required in today’s landscape. And as product lines, partners, and jurisdictions evolve, adopting a modular banking infrastructure fintech approach ensures compliance capabilities can adapt in lockstep with business change. Companies like FlexM demonstrate how long-term compliance strength is built not through scattered tools, but through unified, scalable infrastructure that empowers fintechs to grow confidently. To learn more visit flexcomply.flexm.com or flexm.com.
Global regulators are taking a firmer stance as financial crime grows more complex and harder to detect. Recent enforcement actions have shown how quickly compliance gaps can escalate into major reputational and financial damage. Whether it is FinCEN issuing a USD 3 billion penalty to a leading North American bank or FINTRAC issuing $600K fine to a Canadian bank for failing to submit suspicious transaction reports, the pattern is the same: regulators expect stronger controls, real-time oversight, and auditable intelligence across every customer and transaction touchpoint.
For banks and fintechs, choosing the best AML compliance software in 2026 has become essential to protecting customer trust and maintaining regulatory confidence. Compliance is no longer just an operational requirement. It is a strategic defence against penalties, reputational loss, and operational disruption. This is where platforms like FlexComply, the award-winning, 360-degree compliance solution from global fintech leader FlexM, deliver meaningful value by offering a modular and intelligent ecosystem that helps institutions not only stay compliant but dramatically reduce the reputational fallout and financial exposure associated with regulatory penalties.
The Evolving Landscape of AML Automation for Financial Institutions
Today’s financial ecosystems span cross-border payments, embedded finance, digital wallets and real-time settlement environments. With every transaction carrying potential risk, manual reviews and disconnected systems simply cannot keep pace. This is why AML automation for financial institutions has become a foundational requirement for modern compliance teams.
The global digital payments market is projected to reach USD 19.89 trillion by 2026, growing at a CAGR of 24.4%. As transaction volumes accelerate, regulators are demanding more rigorous controls: smarter analytics, continuous monitoring and fully auditable reporting.
Key Capabilities That Define the Best AML Compliance Software
Modern compliance technology must do more than detect suspicious activity. The best AML compliance software in 2026 will be defined by following foundational capabilities:
- Unified Risk Intelligence – Integrating KYC, sanctions screening, transaction monitoring and customer risk scoring into one dashboard reduces false positives and improves visibility.
- Real-Time Transaction Monitoring Automation AML – AI and behavioral analytics enable institutions to detect unusual activities across borders and currencies instantly.
- Modular Scalability – A flexible AML solution platform for banks & fintechs should allow rapid adaptation to new regulations or geographies through API-first integration.
- Audit-Ready Reporting and Transparency – Generating Suspicious Transaction Reports (STRs) and audit logs automatically ensures accuracy and accountability.
Platforms like FlexComply already embed these capabilities within a unified, modular ecosystem—bridging innovation and regulation to help institutions stay one step ahead of evolving financial crime risks.
From Manual Oversight to Intelligent Automation
Traditional compliance teams spend a major chunk of their time on manual alert reviews and data collection, which creates inefficiencies—not only in manpower hours but also in the ability to detect evolving risks effectively. As financial ecosystems grow more complex, these manual processes can no longer keep pace with the volume and velocity of transactions.
This is where automation becomes the cornerstone of digital transformation. Intelligent transaction monitoring automation AML systems use behavioral analytics to learn from patterns across geographies, currencies, and counterparties. Instead of static rule libraries, they dynamically adapt to new typologies. These innovations give compliance analysts back their time to focus on investigation, not noise. And for customers, it translates to smoother onboarding, fewer verification delays, and greater trust that their data is handled securely and ethically.
AML Automation for Financial Institutions
The global AML market size is projected to grow to USD 9.38 billion by 2030 at a CAGR) of 17.8% — selecting the right AML software in this environment means looking beyond buzzwords. The evaluation criteria should center on adaptability, scalability, and explainability. Does the platform support multilingual, multi-jurisdictional compliance? Can it be deployed as a white-label solution for fintechs or integrated seamlessly into existing digital ecosystems? Is it continuously learning from transactional behavior? The best AML compliance software in 2026 will not be static—it will evolve alongside the threats it combats.
The companies that adopt a unified AML solution platform for banks & fintechs—backed by explainable AI, cross-module orchestration, and secure scalability—will not only meet compliance standards but exceed customer expectations.
By the time the next wave of regulations arrives, institutions that invested early in intelligent compliance will already be ahead. They will have built systems that learn continuously, adapt instantly, and protect both business integrity and customer trust.
The New Standard for Compliance Excellence
In 2026, compliance is no longer a checkbox—it is a strategic differentiator. Intelligent AML automation for financial institutions will determine which institutions thrive in an era of real-time, AI-powered finance.
Early adopters will operate with systems that learn continuously, respond instantly and withstand regulatory scrutiny—protecting both institutional integrity and customer experience. FlexComply’s modular, intelligence-driven design reflects this vision, empowering financial institutions worldwide to reduce compliance risk, strengthen regulatory trust and protect their brand reputation with confidence. To learn more visit flexcomply.flexm.com.


Where We Made the Difference
The solution was devised as not only a way to embrace digital but also to create a unique model to offer cashback at offline merchants. This enabled the offline retailers to match their online shopping counterparts in creating customer loyalty by integrating proven contactless solutions.

The Agrani Remit app is an excellent example of how digital innovation helped the Bangladeshis working in Singapore to digitally and conveniently remit money, back to their family members safely…

FlexM, one of our collaborative partners, played a crucial role in conceptualizing the solution (FlexM's Compliance Solution). Their continued support throughout this transition has been invaluable. We are grateful for FlexM's significant contribution to the solution and their unwavering support as we navigate this transition.

FlexM offers invaluable (RegTech) services for monitoring our card transactions and reporting to the RBI. Their expertise and commitment to excellence have significantly enhanced our compliance and risk management processes.